
Gridinsoft 在 glacat.com 上观察到的情况
Gridinsoft 威胁分析师直接检查了该网站,并记录了支持此决定的证据。
GMA-20261021151406-031cbace
- 检查时间
- 由 Gridinsoft 威胁分析师 完成
- 分析师结论
- 公共 URL 缩短与文件分享服务 — 需要审查精确对象
- 证据依据
- 第一方网站分析 外部安全厂商情报: 仅作背景参考——未用于本次决定
当前独立审查未在 glacat.com 上复现活跃 phishing 或 malware 对象。最新 Gridinsoft 结果未指出具体有害对象;根路径和公开页面呈现其声明的服务,公开来源发现的 28 个精确短链接目前都返回 HTTP 404 且不跳转。公开 urlscan 记录保存了历史代码跳转到无关且类似支付或品牌的路径,这证明了对象级历史滥用;但可用捕获没有显示特定凭据接收端、malware payload、文件或 hash。外部域名 blacklist 标签和 OTX 关系只是背景,未确定当前 sample。由于完整的活跃、私有、未索引、已删除和未来用户控制空间无法枚举,不能对整个域名作 Safe 结论。现有 Suspicious Website 分类与这一依赖精确对象的 inconclusive 结果一致,没有依据更改。
分析师结论
本次检查记录了 8 项观察 查看证据
最新受支持的 Gridinsoft 结果访问 glacat.com 服务根路径并得到 HTTP 200,未显示正向有害行为信号。结果未指出精确凭据接收端、无关 redirect、automatic download、malware 文件、payload、exploit、命令或 hash。Suspicious Website 是宽泛警示,并非断言每个短链接或托管对象都有害。
- 公开证据 URL https://gridinsoft.com/online-virus-scanner/url/glacat-com
-
HTTP 状态
200 - 页面元素 The fresh result contained no positive behavior signal.
- 分析师观察 The fresh result did not name a concrete harmful glacat.com URL, destination, file, payload, receiver, command, exploit, or hash.
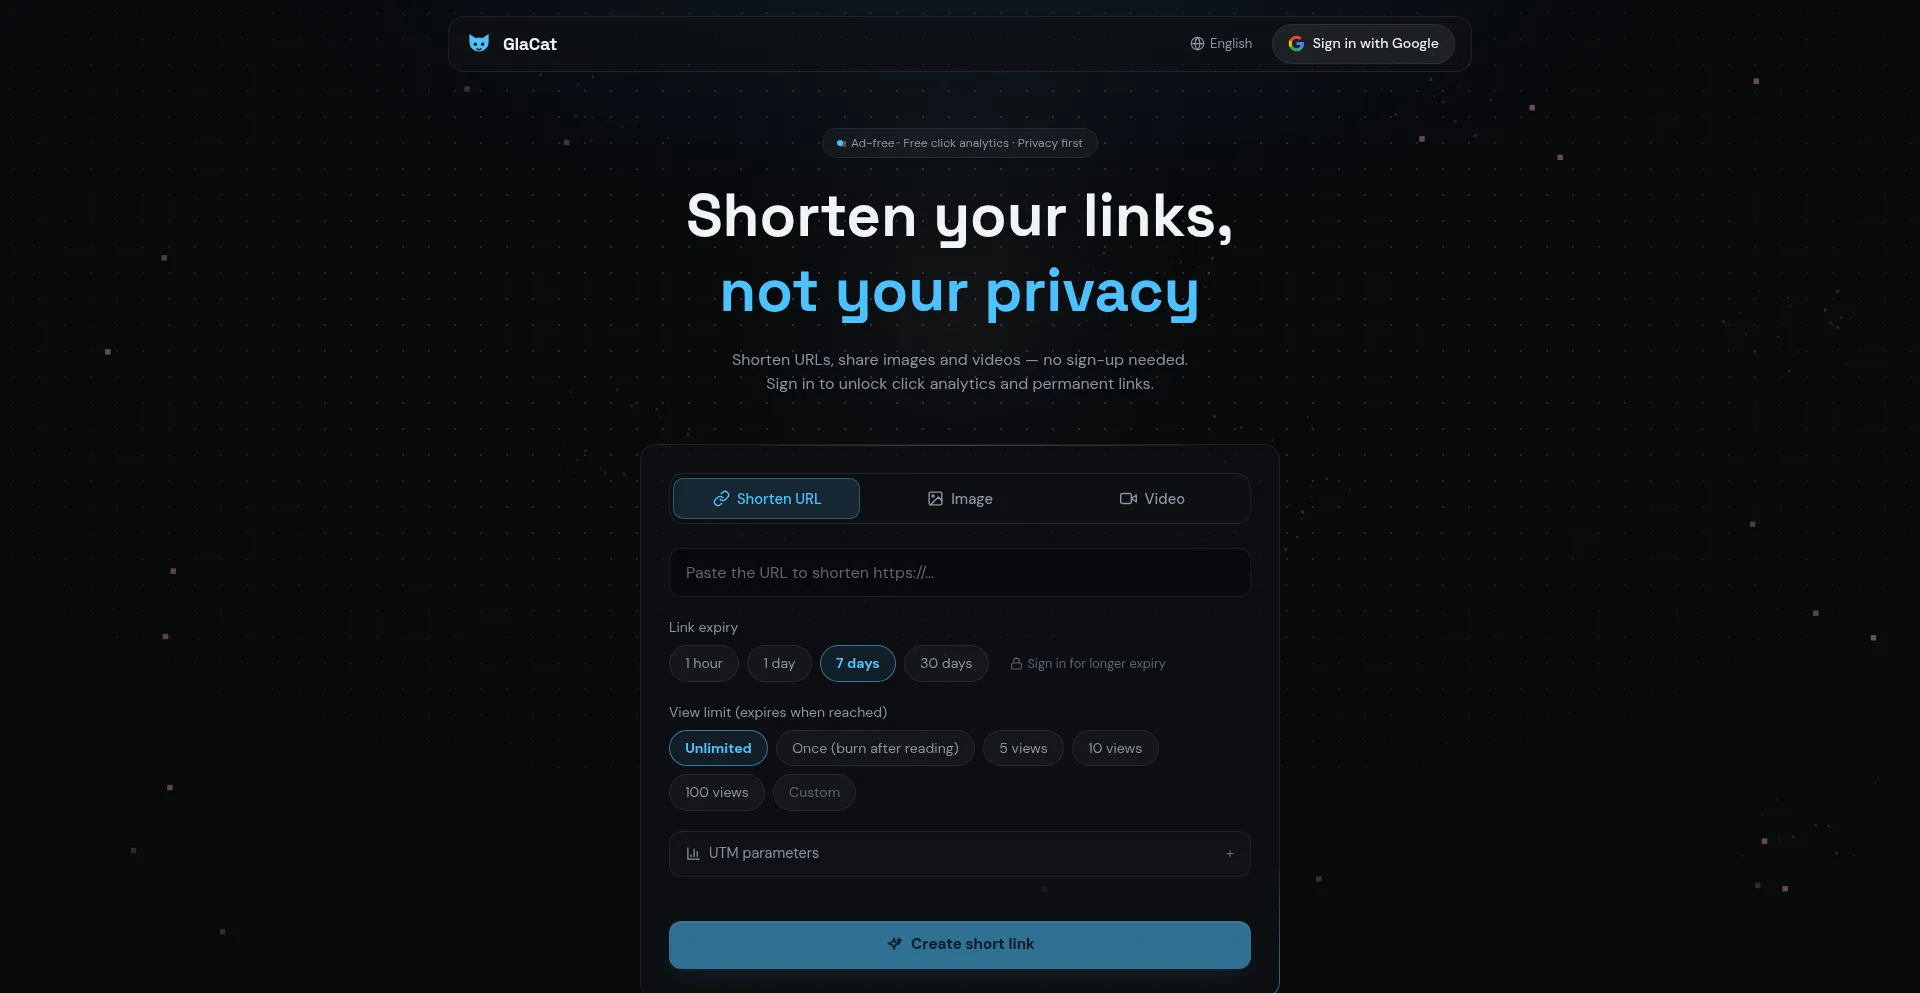
apex 及 security、no-ads、burn、share、about、privacy 和 terms 公开页面均返回 HTTP 200,并一致将 GlaCat 描述为用户控制的 URL 缩短及文件、图像和视频分享服务。根路径和这些页面没有跳转到无关 host、索取提供方之外的 credentials、触发 executable 或 archive download,也未暴露 malware payload。关于 URL checks、rate limits、Turnstile 和 abuse reports 的内容是运营方声明与可见 controls,并非对每个对象都有效的独立证明。
-
HTTP 状态
200 - 页面元素 The public interface offers URL shortening and file, image, and video sharing.
- 页面元素 The security page describes URL checks, creation rate limits, Turnstile, and an abuse-report address.
- 分析师观察 No unrelated redirect, non-provider credential request, executable or archive download, or malware payload was observed on the reviewed root and public information pages.
使用 desktop、mobile、crawler 和 Gridinsoft-review profiles,直接检查了公开 URL intelligence、历史 captures 或 exact search 找到的 28 个精确代码。所有代码目前都返回相同的 GlaCat HTTP 404 响应且没有 Location header。没有代码暴露 redirect、credentials 接收端、downloadable file、malware payload 或 hash。这支持已知公开对象已删除或过期,但不能枚举全部私有或未索引代码和文件。
-
HTTP 状态
404 - 分析师观察 All 28 known codes returned HTTP 404 without a Location header across five request profiles.
- 分析师观察 Checked codes: /uGB03mp, /uJzoyJ3, /uL39GYn, /u2X8WA2, /uvfJCpg, /usyZb2i, /uE1z7vD, /u8tpyYn, /uE22eyb, /uMSx1nw, /uI3qoMN, /uBBwrod, /uFtOVeI, /unIgFpC, /ufmkyoE, /uCoW7sC, /uymMmVo, /uxAXjBn, /uDLa5I1, /uOClpWB, /uSzCJEJ, /u3WDt8h, /ubNU3fL, /uGC3Kcu, /uZcXIvH, /uSrlY37, /ukhx9LJ, and /uCvBJmF.
- 分析师观察 A synthetic nonexistent code also returned the same HTTP 404 response and no redirect.
2026 年公开 urlscan captures 保存了精确 GlaCat 代码通过 HTTP 302 跳转到无关 hosts 和类似支付或品牌的路径。代表性 destinations 包括 mdmh-pinebluff.com、rngtechindia.com、eurobank.s-host.net、eopyy.s-host.net、bingo-cafe.com、bingo-kaffee.com、bingo-coffee.com 和 crowhurst.com.au。审查时可用的最终页面显示 hosting bot block 或 HTTP 404,而不是已捕获的 credentials 表单或 malware delivery。这是可复现的对象级历史 redirect abuse 证据,但未证明具体 phishing payload、接收端、malware 文件或 hash;相关代码现在返回 HTTP 404。
- 公开证据 URL https://urlscan.io/result/019d6d43-f5b0-73cc-81d6-5500caed9423/
-
重定向目标
https://mdmh-pinebluff.com/r/50ooO3O7 -
重定向目标
https://rngtechindia.com/pay/pLF9LD52 -
重定向目标
https://eurobank.s-host.net/KQxXmItm -
重定向目标
https://eopyy.s-host.net/pay/BjQ21x6L -
重定向目标
https://bingo-cafe.com/QOQpz2xb - 分析师观察 The preserved scans demonstrate historical exact short-link redirects to unrelated hosts, while the available final-page captures showed a bot block or HTTP 404 and did not expose a credential receiver, malware payload, file, or hash.
提交的精确 host 与可注册 parent domain 是同一 apex glacat.com。urlscan 报告 2,741 次公开 scans,并提供精确对象的历史 redirect 证据;近期结果集中于少数已停用代码,且没有 malicious urlscan verdict。OTX 为 apex 保留 16 个 PhishDestroy pulse associations 和十条 URL observations;www.glacat.com 没有 DNS 响应。当前 URLhaus、OpenPhish、Phishing.Database、ThreatFox 与 PhishDestroy active feed 快照无精确匹配。
- 公开证据 URL https://urlscan.io/domain/glacat.com
- 公开证据 URL https://otx.alienvault.com/indicator/domain/glacat.com
- 公开证据 URL https://web.archive.org/web/*/glacat.com/*
- 分析师观察 urlscan reported 2,741 public scans; OTX retained 16 PhishDestroy-related pulse associations and 10 URL observations.
- 分析师观察 The current public URLhaus, OpenPhish, Phishing.Database, ThreatFox, and PhishDestroy active-feed snapshots contained no exact glacat.com match.
- 分析师观察 Exact-host and parent-domain OSINT refer to the same glacat.com apex; www.glacat.com did not resolve.
Wayback 返回 114 条 apex 合并记录和 218 条 wildcard 记录。2021 年根路径快照属于此前的 parked-domain lifecycle;2024 年起的快照显示 GlaCat 服务。2024 年一个 archived exact code 返回 structured not-found response 而非 redirect。archive 未在 apex 保存精确 credentials 表单、malware 文件、payload 或 hash,但其 coverage 有限,无法枚举私有、已删除或未记录的链接和文件。
- 公开证据 URL https://web.archive.org/web/*/glacat.com/*
- 分析师观察 Wayback returned 114 collapsed apex records and 218 wildcard records.
- 分析师观察 The 2021 root was parked under an earlier lifecycle; snapshots from 2024 onward presented the GlaCat service.
- 分析师观察 The archived exact path /uBBwrod returned a structured not-found response with no redirect destination.
当前外部 snapshot 保留十三个 malicious 和一个 suspicious result。负面 engines 使用 domain blacklist methods,并给出 phishing、malware、malicious 或 suspicious labels;Avira、Norton 和 Bitdefender 另有 warnings。可用记录未指出导致标签的精确 active URL、response、receiver、file、payload 或 hash。它们说明 reputation disagreement 与 historical context,而非可复现的当前 harmful object。
- 页面元素 External snapshot: 13 malicious and 1 suspicious domain-level results.
- 分析师观察 The adverse engines used blacklist methods and did not name an exact currently active glacat.com URL, response, file, payload, receiver, or hash.
- 分析师观察 Domain-level blacklist categories are distinct from a captured exact URL with observable harmful behavior.
glacat.com 是用户控制的公共短链接与文件 namespace。根路径提供 creation interfaces,但没有活跃、私有、已删除或未来代码和文件的完整 directory。已发现并审查 28 个精确公开代码,但关键 namespace 无法独立枚举。有限 clean 样本和运营方声明的 controls 不能支持整个域名的 Safe certification。未来 findings 应检查 exact short URL 或 hosted object 及其可见 destination 或 content。
- 页面元素 The root exposes public URL-shortening and file-sharing creation interfaces but no complete object directory.
- 分析师观察 Twenty-eight known public codes were reviewed, but the complete current, private, deleted, and future namespace was not publicly enumerable.
- 分析师观察 A domain-wide Safe verdict cannot be inferred from a clean root or a finite set of disabled user-controlled objects.
范围与限制
- 提交的精确 host 即可注册 parent domain;host 与 parent OSINT 都指向同一 apex glacat.com。另行检查了不存在的 www alias。
- 审查覆盖最新 Gridinsoft 结果、根路径和七个 public pages、28 个 exact short codes、desktop、mobile、crawler 与 review profiles、DNS、TLS、URL 与 threat intelligence、active feeds、historical captures 和 archives。
- 完整 current、private、unindexed、deleted 与 future 代码和文件 namespace 无法公开枚举。已审查 28 个已知对象;不对未观察对象作结论。
- 历史 urlscan records 保存了到无关 hosts 的 redirects,但可用 final captures 显示 bot block 或 HTTP 404。因此不声称捕获了具体 credentials receiver、malware file、payload 或 hash。
- 关于 security、rate limits、Turnstile 与 abuse reports 的内容被记录为 operator claims 和 visible controls;其对每个对象的有效性未经独立验证。
- Conditional、geographic、account-bound、language-dependent、referrer-dependent、device-dependent 或 time-limited content 可能在已审查 profiles 和 locations 之外不同。
- Public search、urlscan、OTX、archives、feeds 与 sandbox indexes 都有限。没有 active matches 不能证明历史上不存在 unindexed 或 historical harmful object。
- 历史威胁情报和证书记录并不完整;这些记录中的空缺不能证明安全。
- 外部 blacklist 与 threat-intelligence labels 仍是 independently controlled context。它们不等于 current reproducible malicious URL 或 sample,也未决定 Gridinsoft verdict。
- 该 verdict 不认证每个 current 或 future short link 或 hosted file 为 safe,也不保证以后 content 或 destination 不会改变。


帮助保护他人,快在社交媒体上分享此页面吧!知道glacat.com的人越多,骗子就越难得逞。 在社交媒体上分享此页面,帮助更多人评估glacat.com!