
Gridinsoft 在 Joinrubymd.com 上观察到的情况
Gridinsoft 威胁分析师直接检查了该网站,并记录了支持此决定的证据。
GMA-20260827220842-d68bc385
- 检查时间
- 由 Gridinsoft 威胁分析师 完成
- 分析师结论
- 安全
- 证据依据
- 第一方网站分析 外部安全厂商情报: 仅作背景参考——未用于本次决定
独立第一方审查支持将 joinrubymd.com 的已审查公开部署归类为安全。根域、www 入口、17 条 sitemap 路径、重定向、预约页面源代码、DNS、TLS 以及重复的直接请求均未复现 phishing、凭据窃取、无关自动重定向、自动有害下载、malware 交付或其他恶意对象。更名和服务提供商角色已由当前条款和披露在实质上得到确认;与药物相关的营销内容仍然可见,但它不是此前广泛 Suspicious Website 分类的可复现安全依据。
分析师结论
本次检查记录了 7 项观察 查看证据
审查了 HTTPS 首页和当前 sitemap 中的 17 个 URL。全部 18 个页面在重定向后均返回 HTTP 200 和一致的 RubyMD 内容;/replay-page 仅重定向到同站点 /replay2。未复现无关自动重定向、可执行文件或压缩包自动下载、凭据仿冒或 malware 交付。
-
HTTP 状态
200 -
最终 URL
https://joinrubymd.com/ - 页面元素 Title: RubyMD - Start a Telehealth Business in 30 Days | 100 Clinics Built
- 分析师观察 The root plus 17 sitemap URLs were reviewed; every page returned HTTP 200 after redirects, and no automatic off-domain redirect or executable or archive download was reproduced.
HTTP 根域、HTTP www 和 HTTPS www 入口均汇聚到同一 URL:https://joinrubymd.com/. 重复的直接 HTTPS 请求返回相同最终 URL 和一致内容;目标在重复请求或入口之间没有变化。
-
重定向目标
https://joinrubymd.com/ -
HTTP 状态
200 - 分析师观察 The only observed entry redirects normalized HTTP and www requests to the same HTTPS apex; repeated homepage requests returned identical content.
日期为 2026 年 7 月 18 日的当前条款将 Emberflow LLC 标示为在 joinrubymd.com 以 RubyMD 名义经营的运营方。当前页面链接到 emberflowai.com,隐私页面仍使用 Emberflow。该内容支持所述更名和服务提供商关系。
-
HTTP 状态
200 -
最终 URL
https://joinrubymd.com/terms - 页面元素 Terms identify Emberflow LLC d/b/a joinrubymd.com as RubyMD.
- 分析师观察 Current RubyMD pages link to www.emberflowai.com, and the privacy page retains the Emberflow operator name.
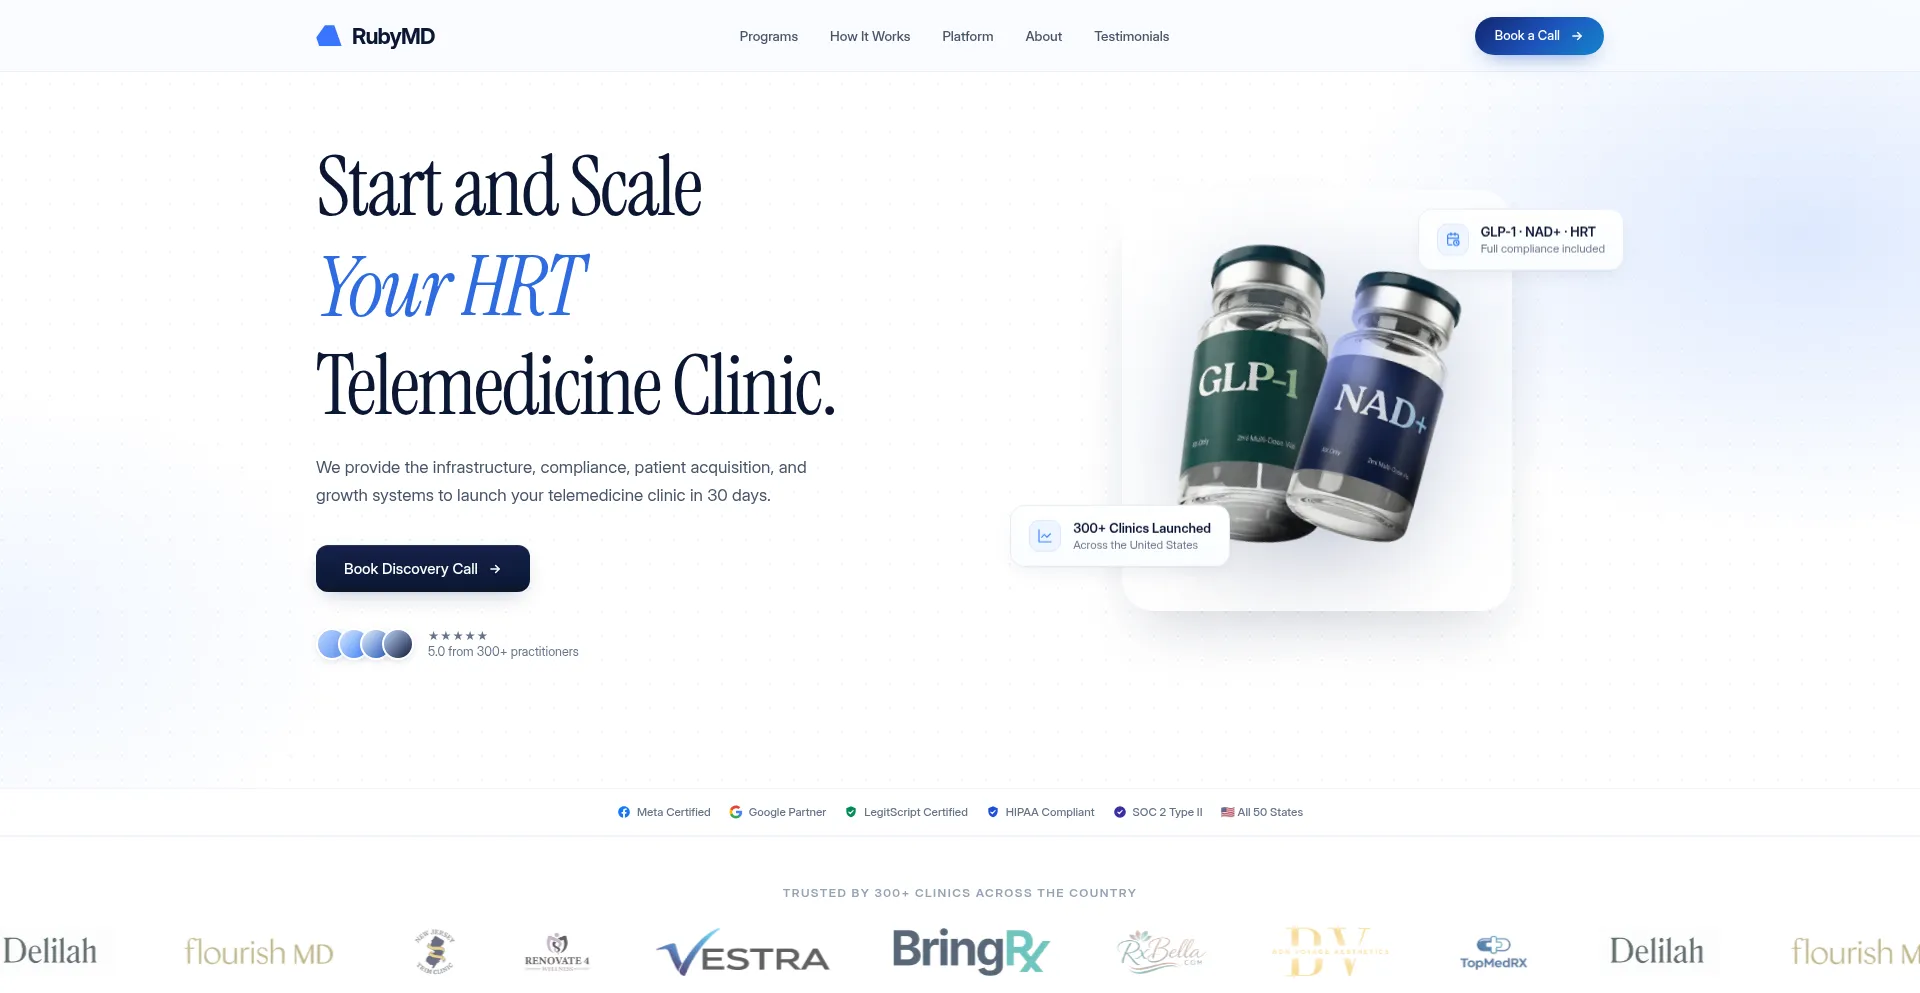
首页表示 RubyMD 提供行政、技术和运营服务,医疗服务由持证服务提供者提供,复配药物只能凭有效处方配发。页面也推广 GLP-1、peptides 和 HRT 诊所基础设施;这些表述不能证明 RubyMD 直接配发药物,也不能证明域名具有恶意。
- 页面元素 RubyMD provides administrative, technology and operational services.
- 页面元素 Medical services are delivered by independent professional corporations and their licensed providers.
- 页面元素 Compounded medications are not FDA-approved and are dispensed only against a valid prescription from a licensed provider.
- 分析师观察 The homepage also advertises clinic infrastructure for GLP-1, peptide, and HRT programs; those marketing references are distinct from observed malware or phishing behavior.
/apply 和 /booking 的源代码通过 LeadConnector 配置预约日历和常规电话输入。未发现密码、一次性代码、钱包恢复、seed phrase、private key、可执行文件上传或自动下载流程;未提交任何表单。
-
最终 URL
https://joinrubymd.com/apply - 页面元素 Appointment-calendar configuration and telephone-input support
- 分析师观察 No password, one-time-code, recovery-secret, private-key, executable-upload, or automatic-download flow was identified in the reviewed public source; no form was submitted.
根域和 www 主机通过 Cloudflare 地址解析并提供已审查网站。Google Trust Services 签发的有效证书分别标示 joinrubymd.com 和 www.joinrubymd.com。共享地址未被视为私有源站或恶意 payload 的证据。
- DNS 信息 joinrubymd.com resolved to 162.159.140.166; www.joinrubymd.com resolved to 104.18.35.90 and 172.64.152.166.
- 证书信息 Apex certificate: joinrubymd.com, valid 2026-08-12 through 2026-11-10; www certificate: www.joinrubymd.com, valid 2026-08-12 through 2026-11-10.
- 分析师观察 Both HTTPS entry points served the expected RubyMD site through shared Cloudflare delivery infrastructure.
新的受支持 Gridinsoft 扫描以 HTTP 200 到达预期 HTTPS 首页。更正前,Suspicious Website 仍绑定到已存储的广泛签名,尽管报告没有正向行为信号,也没有精确恶意 URL、phishing receiver、文件、payload 或 hash。直接审查未复现该警告所需的第一方依据。
-
HTTP 状态
200 - 公开证据 URL https://gridinsoft.com/online-virus-scanner/url/joinrubymd-com
- 分析师观察 The fresh Gridinsoft report contained no current positive behavioral signal and did not identify a specific malicious URL, receiver, file, payload, or hash.
范围与限制
- 判定适用于记录时间内审查的公开根域、www 入口、当前 sitemap 页面和公开源代码;不保证未来或新添加的内容。
- 客户未提供用于精确对象复现的具体恶意 URL、文件、payload、hash、截图或交易。
- 审查未登录私有诊所、患者、服务提供者、药房、管理、计费或广告账户,也未枚举私有、未链接、依赖参数或新创建的路径。
- 已检查预约和咨询配置,但未提交任何表单;未完成付款、医疗接诊、处方、账户或 checkout 流程。
- 审查未验证医疗执照、药房来源、HIPAA、LegitScript、广告、收入、客户评价、临床或法律声明,不构成医疗、监管、隐私或业务绩效认证。



帮助保护他人,快在社交媒体上分享此页面吧!知道joinrubymd.com的人越多,骗子就越难得逞。 在社交媒体上分享此页面,帮助更多人评估joinrubymd.com!